This is an active weekly series for security leaders. Bookmark this page. It grows every Monday. I've spent my career running a security company and w…
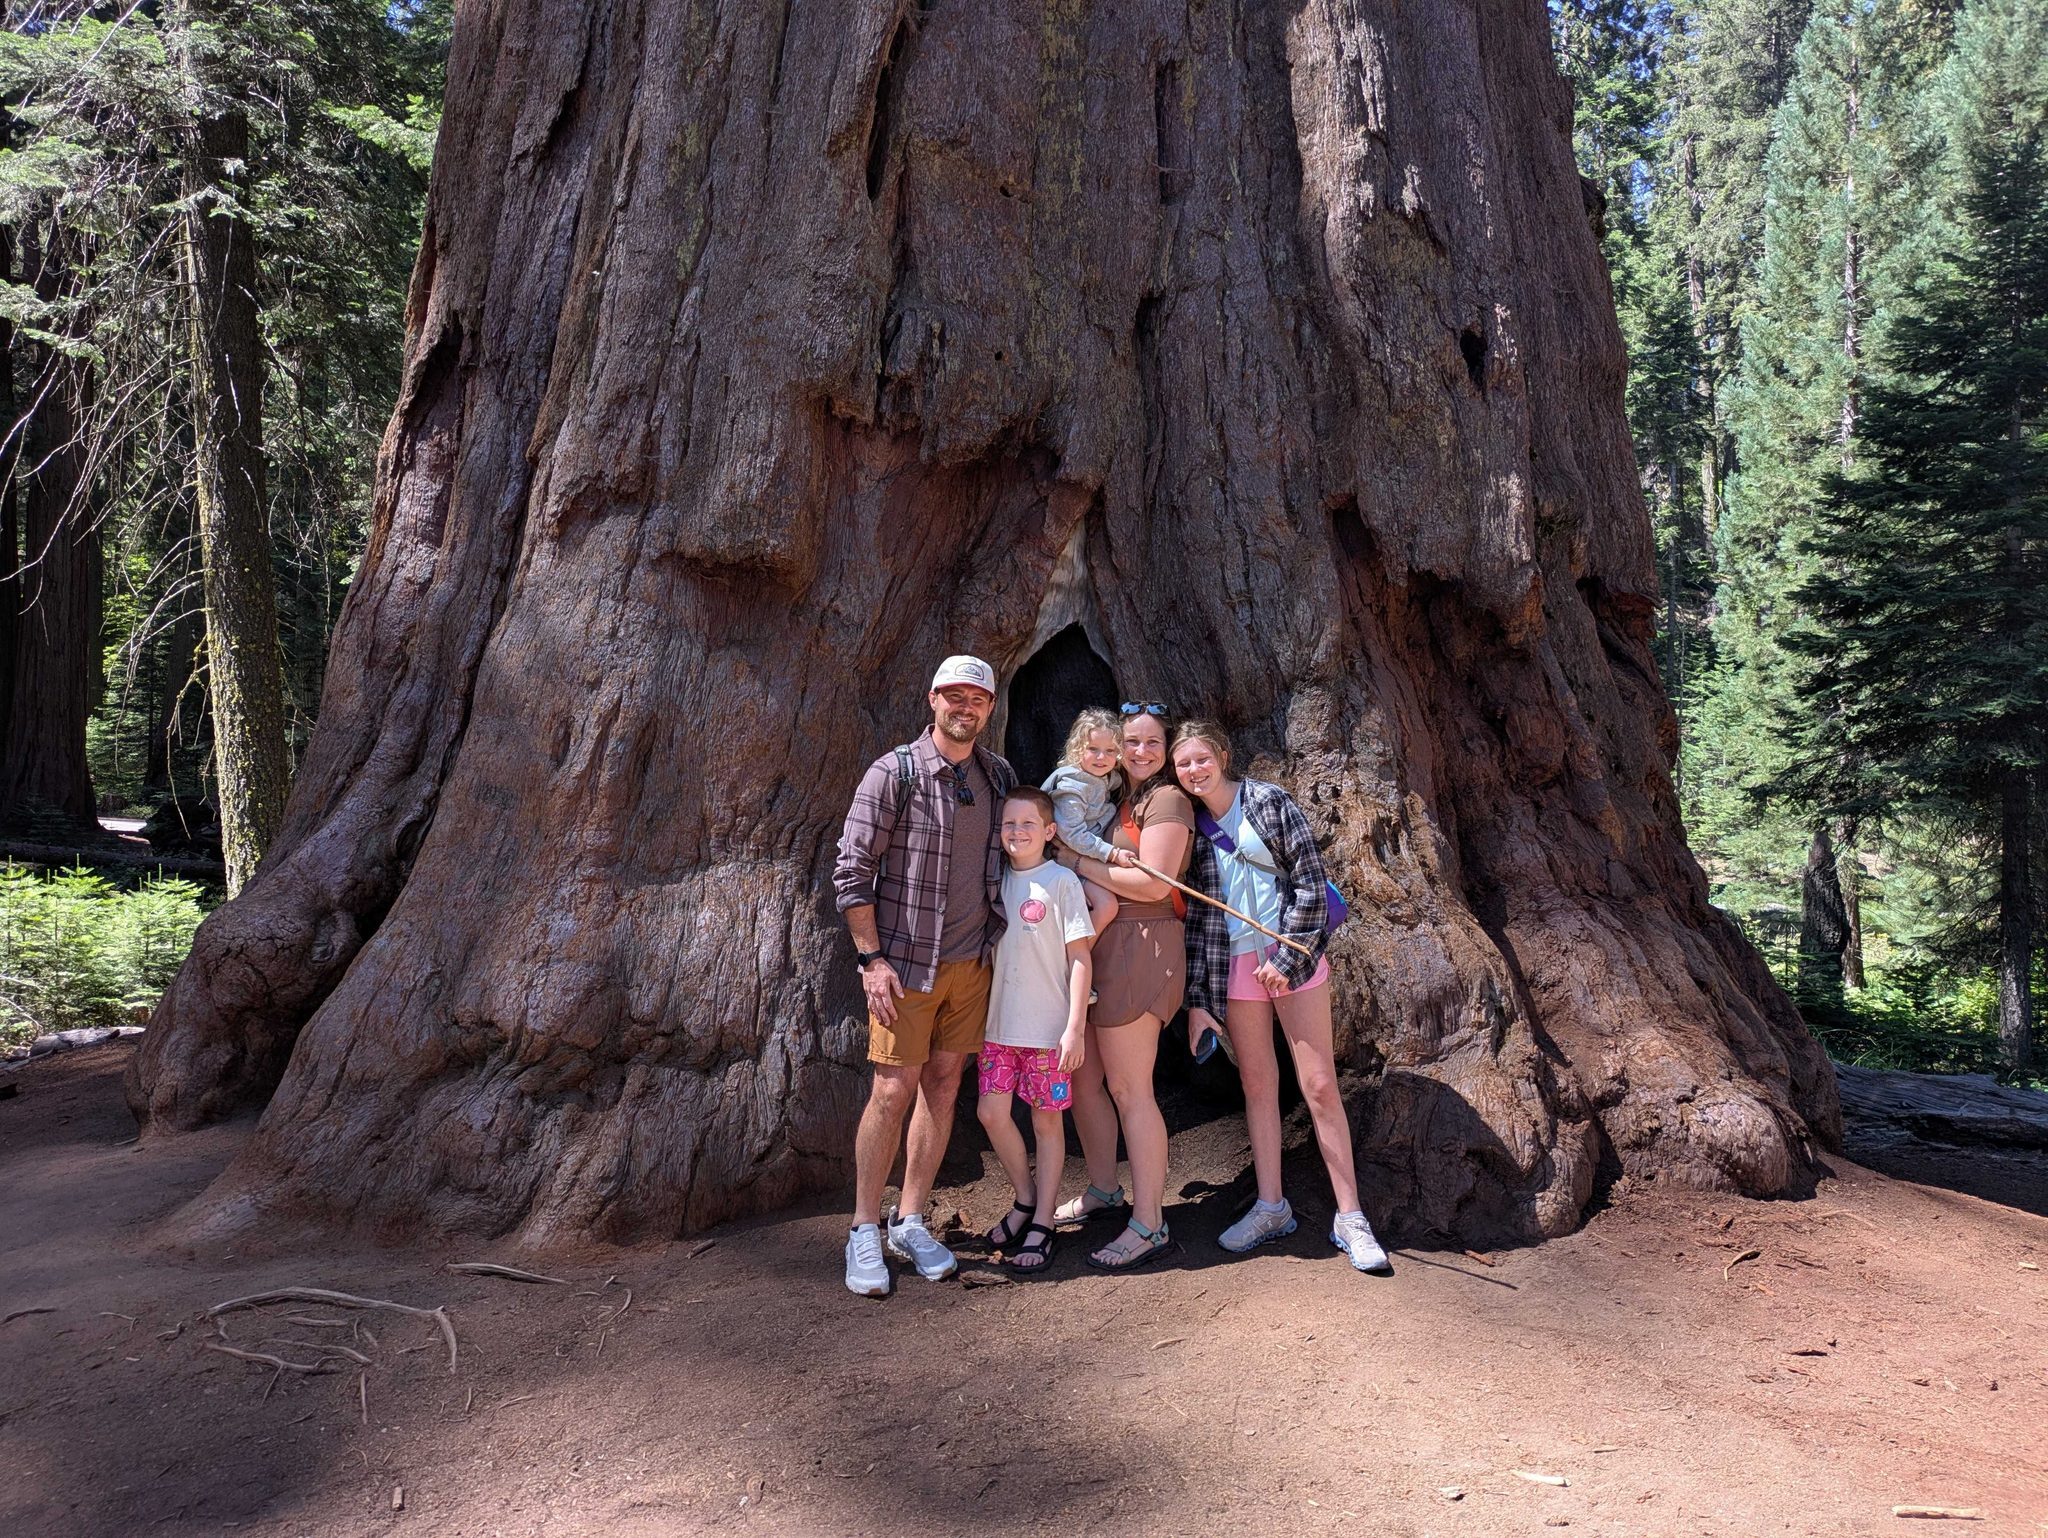
Today is my first day back from a two month Sabbatical. This is a benefit that all of the team members here at risk3sixty enjoy. The way it works is t…
As organizations strive to manage risk and innovation in a rapidly changing AI landscape, the adoption of ISO 42001 becomes increasingly relevant.
This is a joint effort between Schellman and risk3sixty. You can find the original post here.
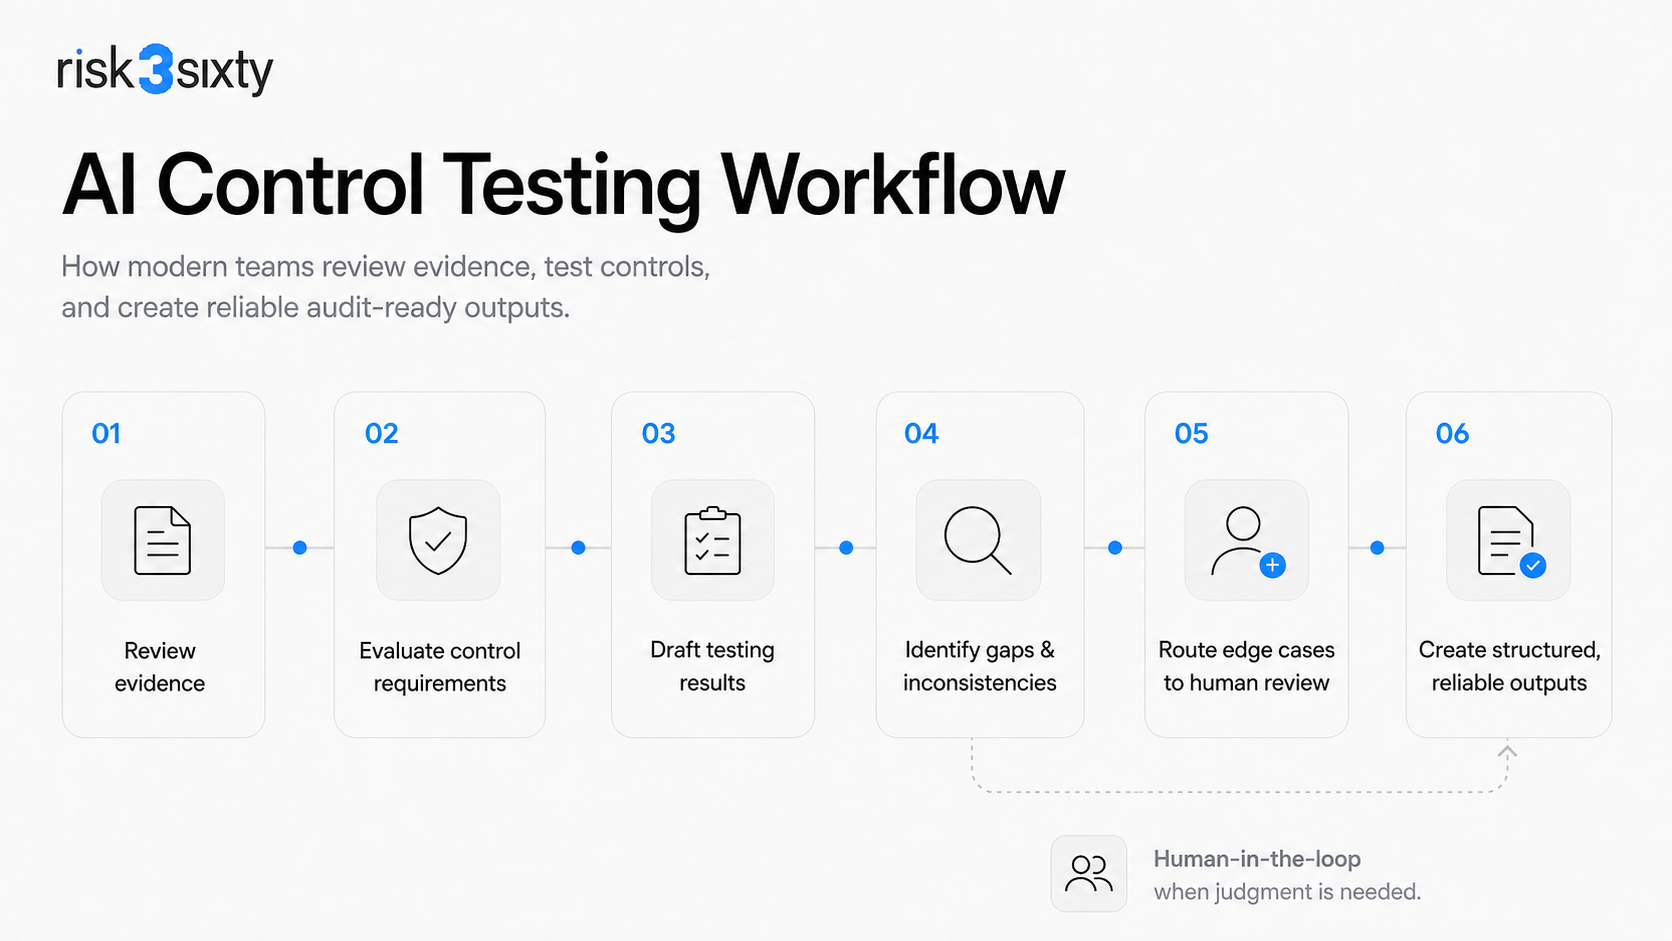
Yesterday I spoke with a team that is responsible for testing 1000s of controls a year. They have an entire staff that goes through the process of gat…
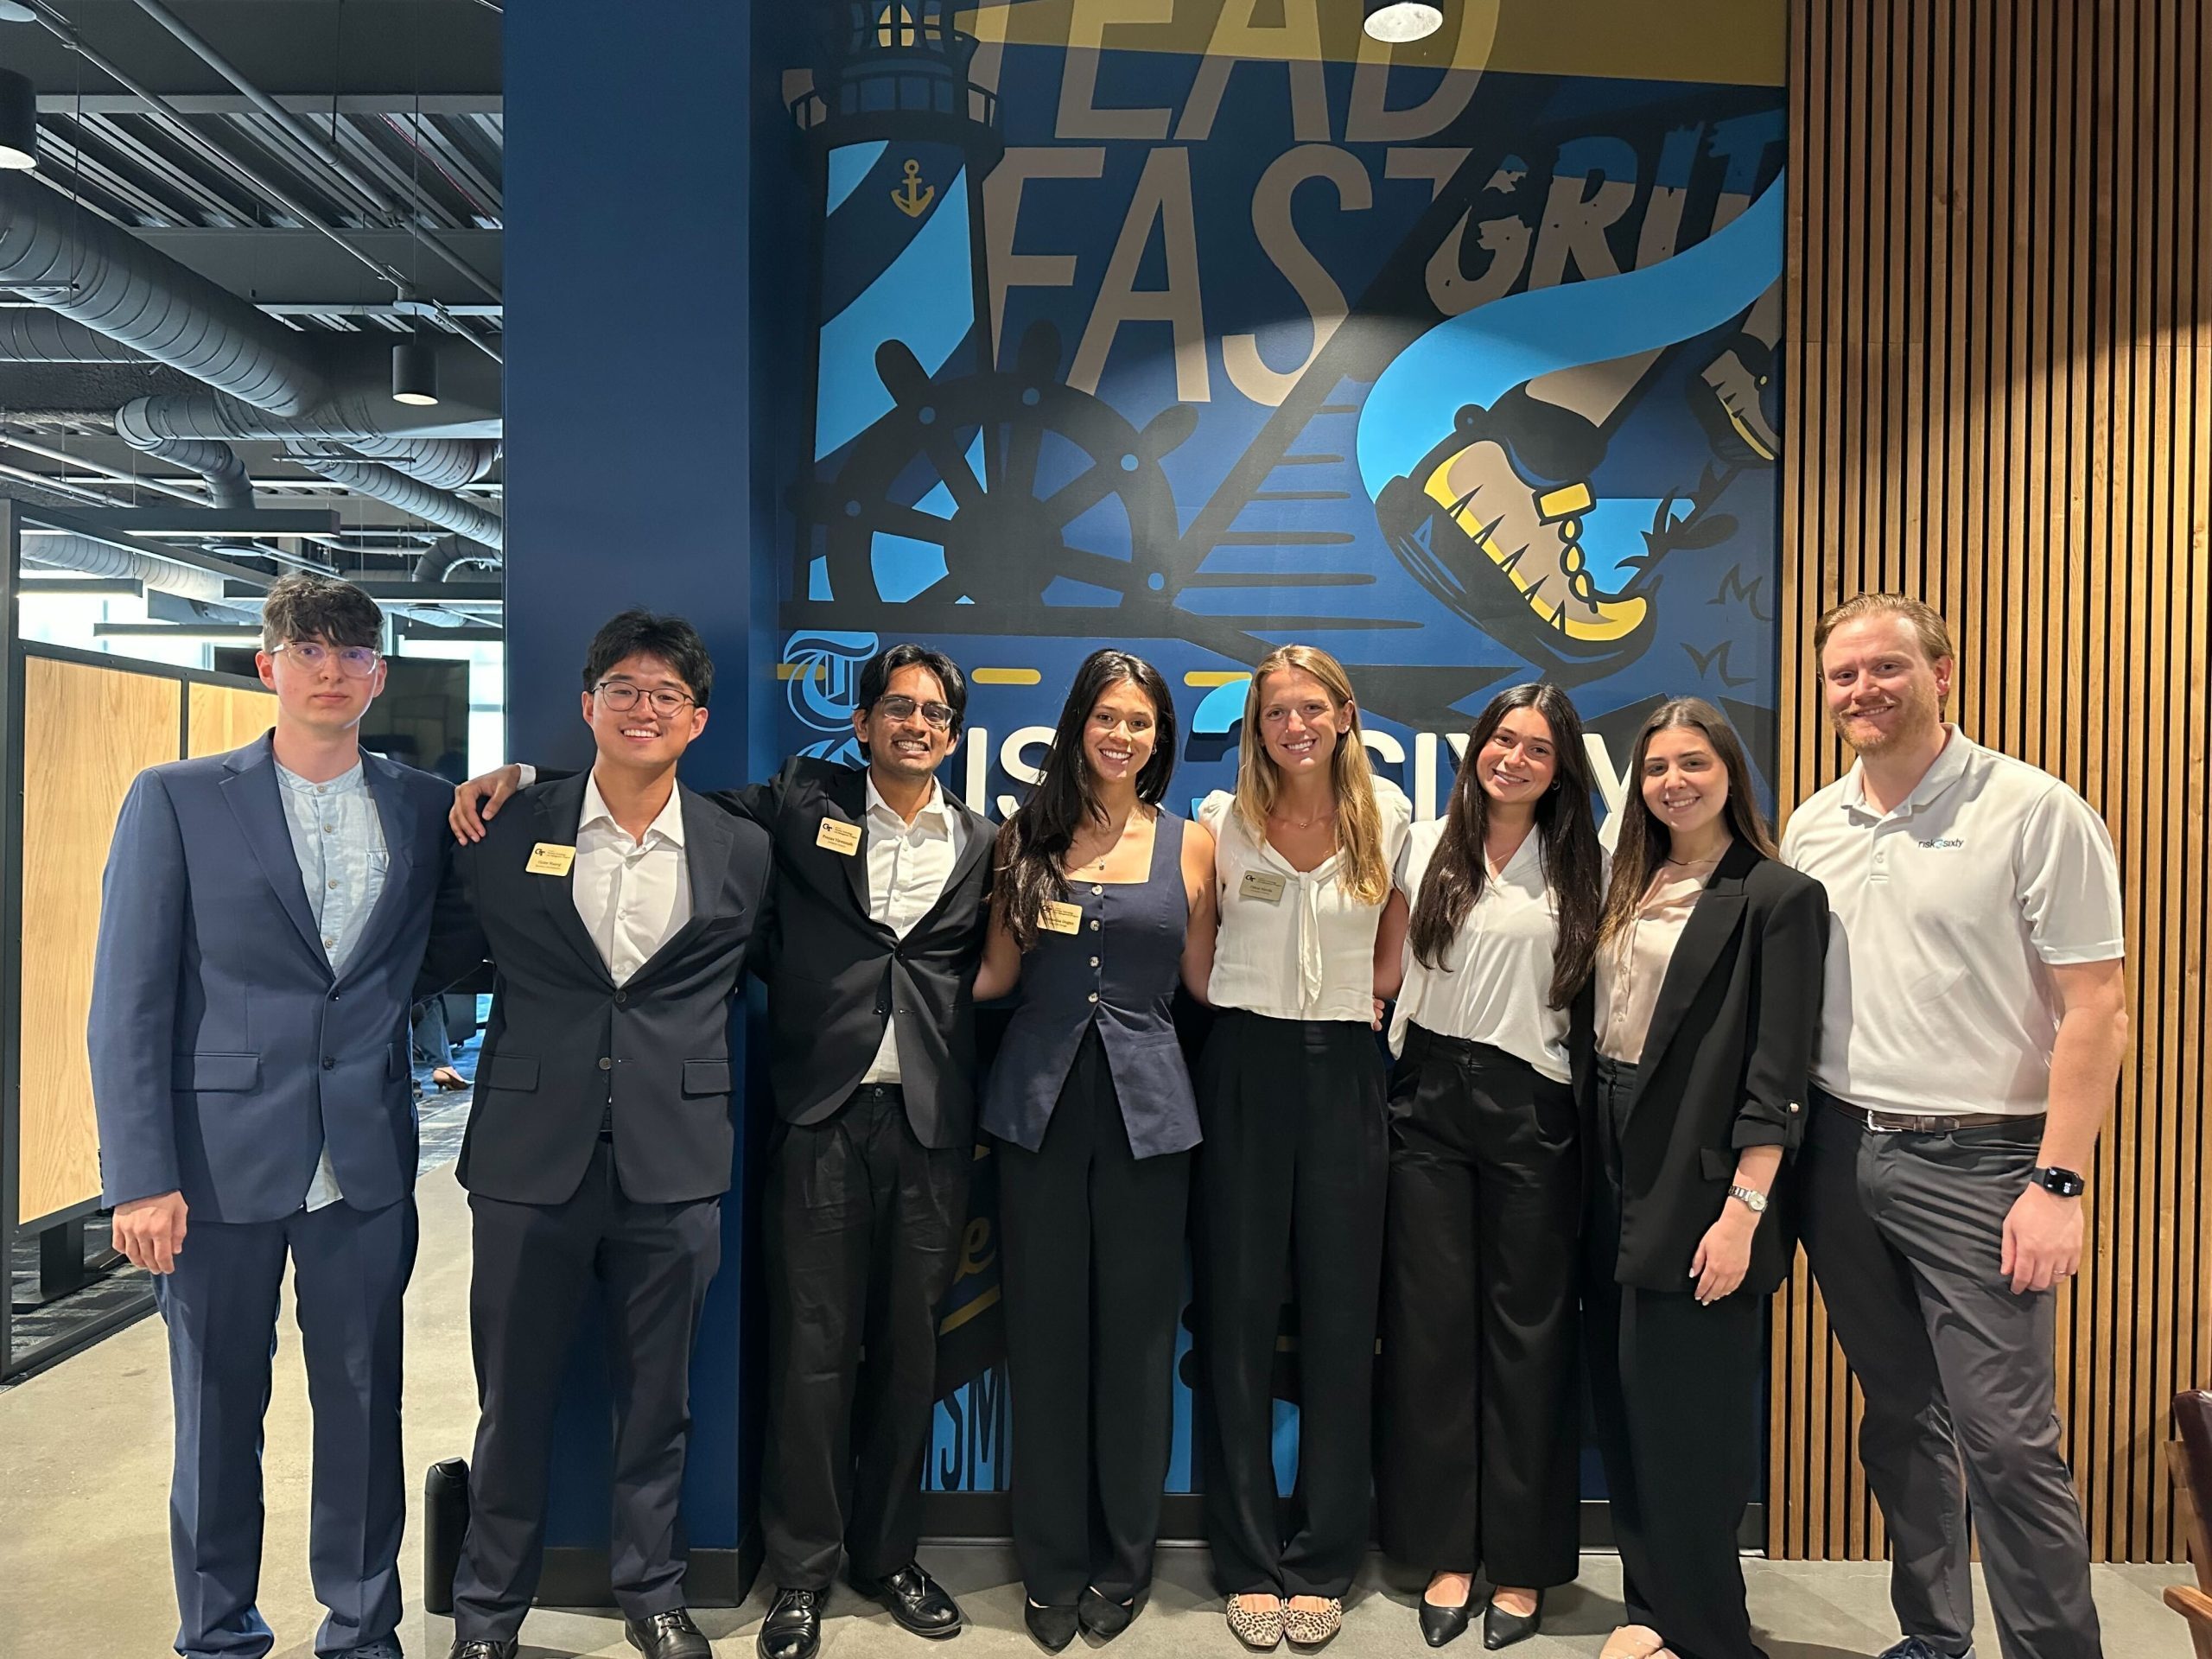
I am blown away by what Georgia Tech students are building right now.
risk3sixty was founded 10 years ago because Christian Hyatt and Christian White wanted to build a business aligned to their personal values. That mean…
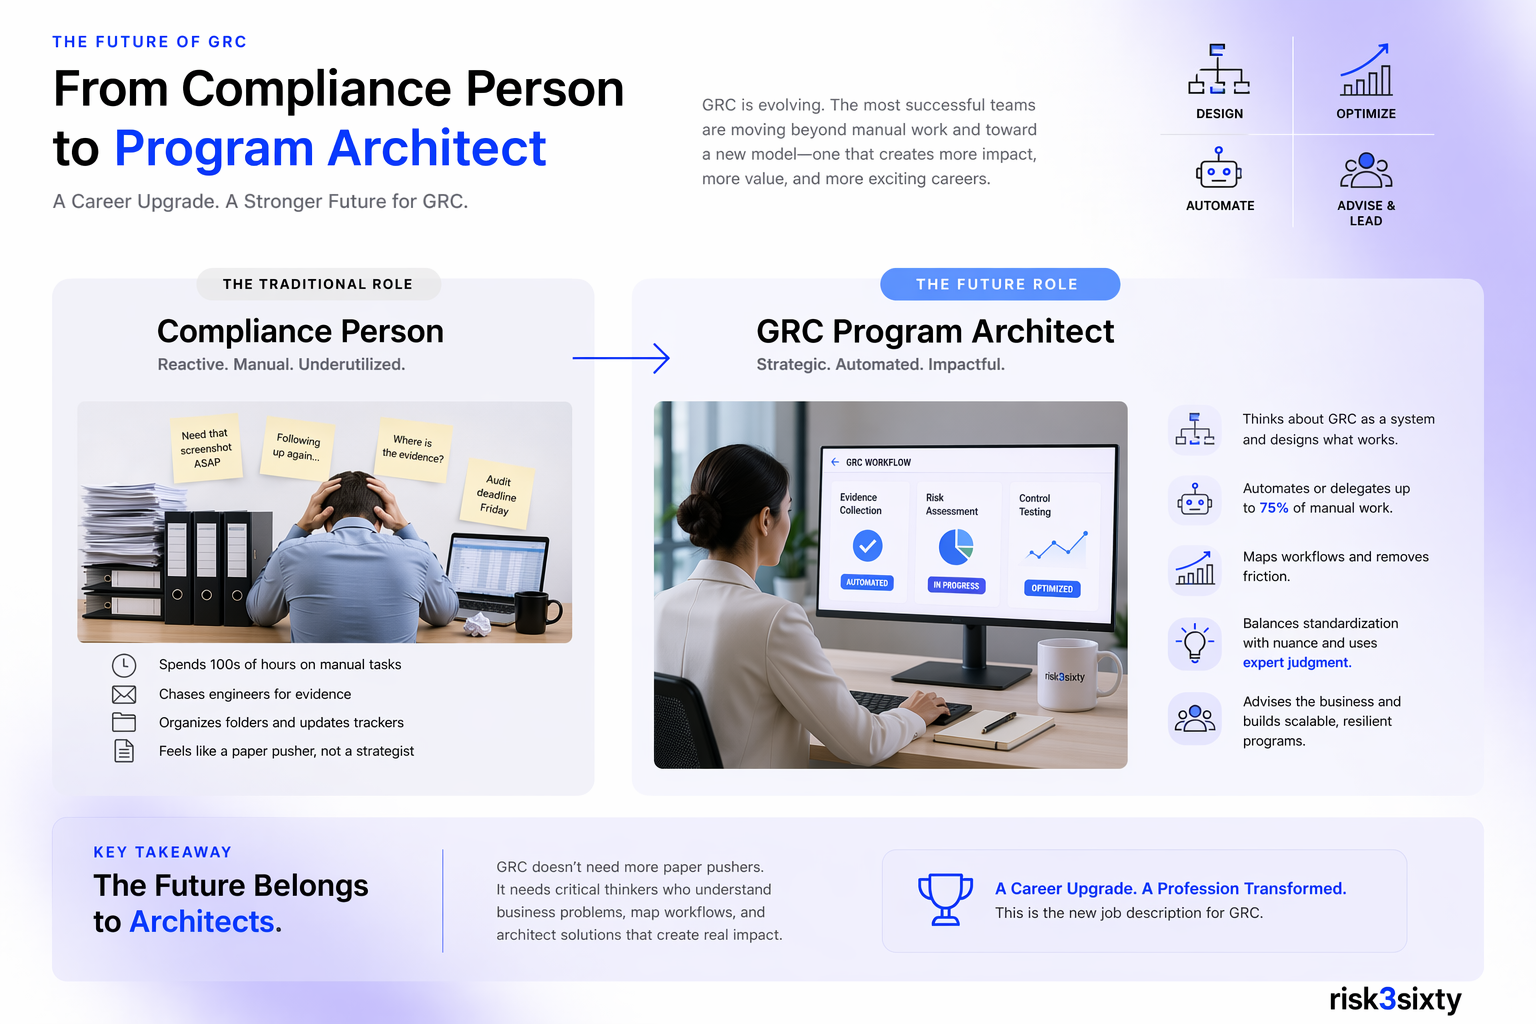
For years, too many talented people entered GRC expecting to do meaningful, high-impact work only to find themselves stuck chasing screenshots, organi…
Most GRC leaders didn’t buy a GRC platform because they were chasing shiny objects or trying to impress the board with new software.
I’ve always been restless. I don’t sit still well. My mind tends to run ahead of me, constantly generating new ideas like services we could launch, im…
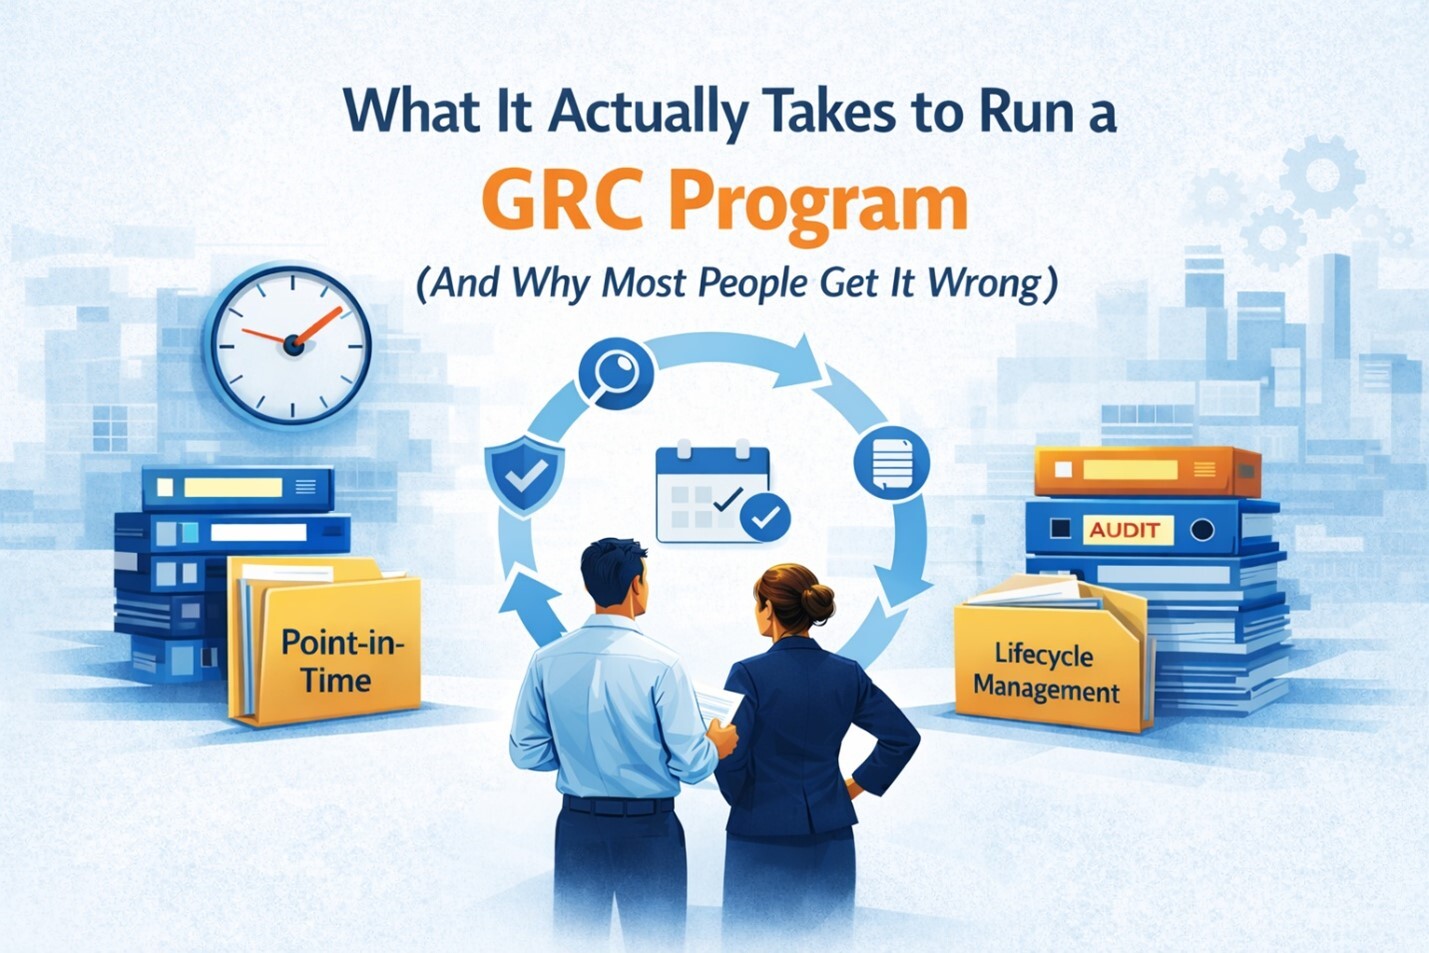
Most people think running a GRC program is about getting ready for audits.