SOC 2
Showing posts tagged with "SOC 2".
Businesses are finding that managing compliance across multiple frameworks is not just a necessity, but a strategic advantage. Harmonizing SOC 2 compl…
Security and compliance are essential in any business environment, and companies often must adhere to multiple overlapping frameworks of security arch…
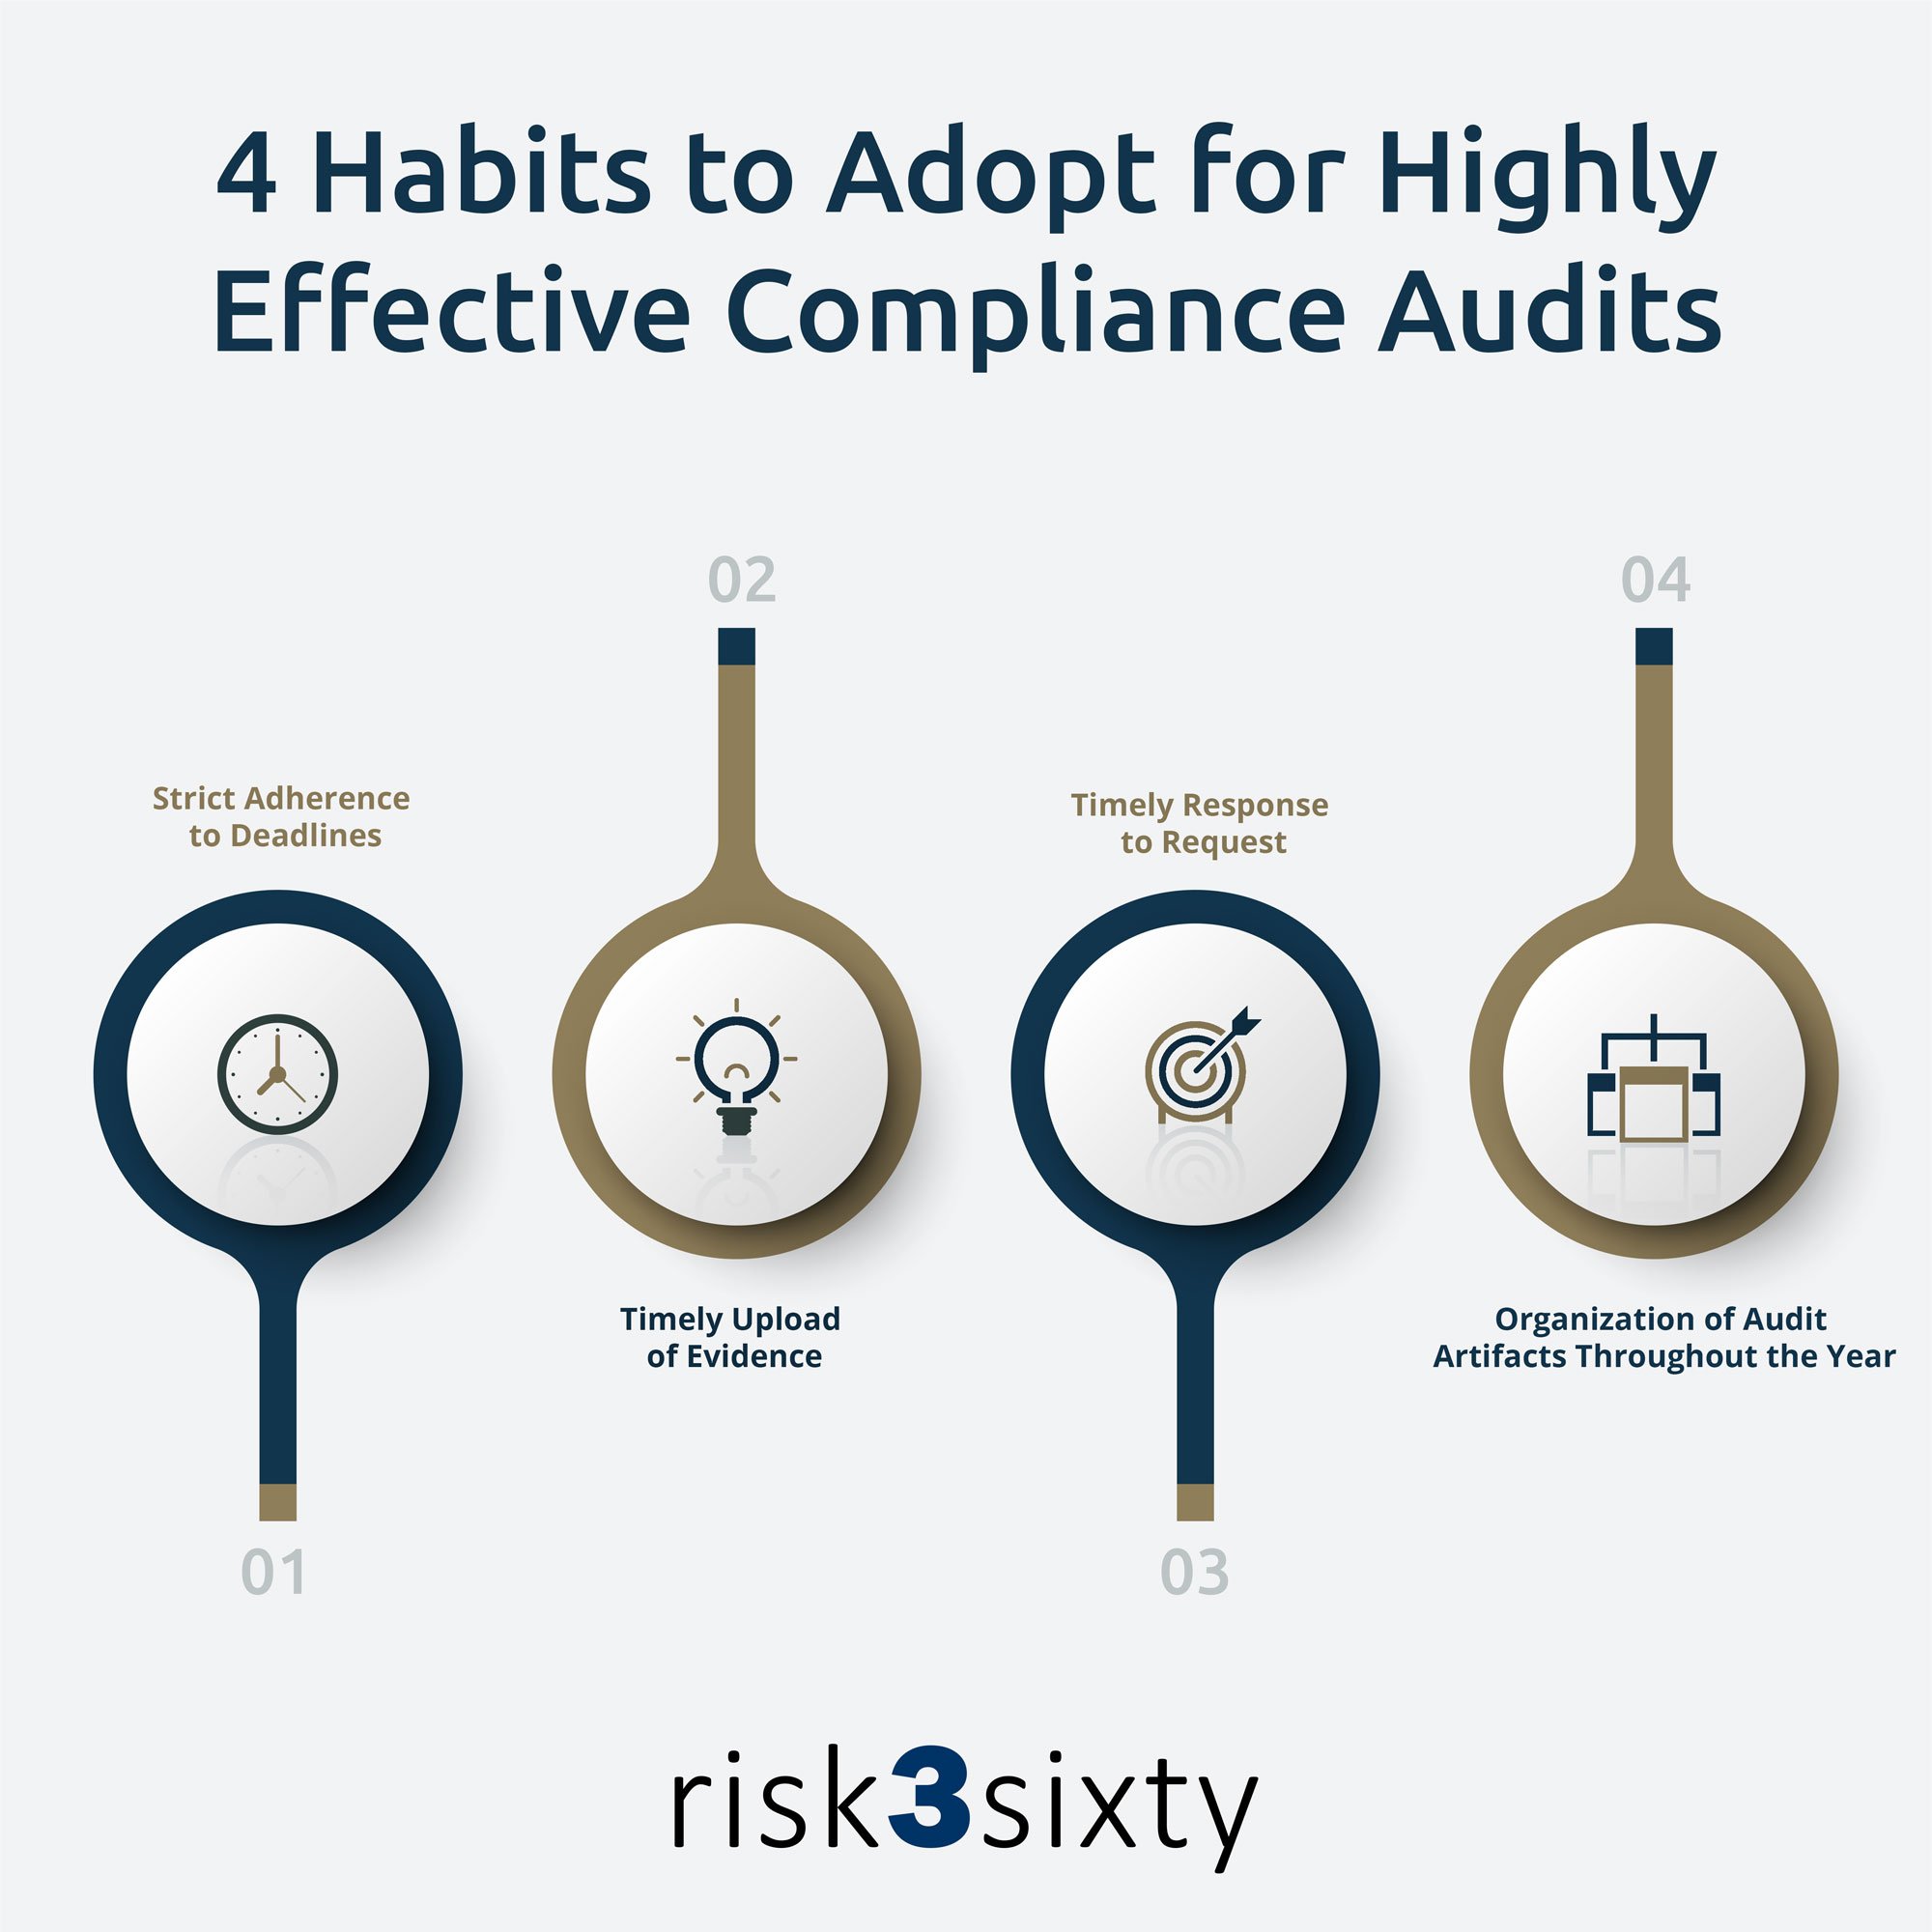
How can you help ensure the successful and timely completion of your compliance audit? This article provides insights into what successful compliance …
The AICPA-designated SOC 2 framework is used to express an opinion on controls over security, privacy, availability, confidentiality, and processing i…
So, you’ve been tasked with providing evidence for an audit. You may be wondering what your auditor is even looking for. Let’s take a look behind the …
Whether you are pursuing an ISO 27001 certification or a SOC 2 report, a robust asset inventory is going to be key to addressing compliance requiremen…
How do you perform a risk assessment, and what do you do with the results? Find answers to some common risk assessment questions in Part 1 of our two-…
In this blog, we’ll dive into one of the most important parts of a SOC 2 report, the SOC 2 System Description! During your due diligence process, a ve…
A guide to the Trust Services Criteria Knowing when to include the various SOC 2 Trust Services Criteria (TSC) (also, criteria) can seem like a daunti…
How can you ensure success for your company’s SOC 2 initiative? Here are 5 Steps to SOC 2 success – best practices and lessons learned from the field!…
If you just received a SOC 2 report and do not know where to start analyzing, this blog is for you! SOC 2 reports can easily reach 50+ pages and can b…
Tags
- Cyber Risk Management (59)
- IT Audit And Compliance (33)
- Penetration Testing (31)
- Cybersecurity (26)
- CISO Discussions (24)
- SOC Reporting (23)
- Security (22)
- News And Events (20)
- Christian Hyatt (19)
- ISO 27001 Compliance (19)
- Risk Management (19)
- ISO 27001 (18)
- SOC 2 (18)
- Compliance (17)
- Business (16)
- HITRUST (16)
- PCI DSS (13)
- Regulatory Compliance (12)
- Information Security (11)
- IT Audit (9)
- Webinars (9)
- CISO (8)
- Privacy (8)
- Penetration Test (7)
- Privacy Compliance (7)
- VCISO (7)
- Business Continuity (6)
- Cyber Risk (6)
- GRC Tool (6)
- ISO 42001 (6)
- Leadership (6)
- Compliance As A Service (5)
- Disaster Recovery (5)
- News (5)
- Risk Assessment (5)
- Training (5)
- BCAW (4)
- Cybersecurity Controls (4)
- GDPR (4)
- Network Security (4)
- Access Control (3)
- Artificial Intelligence (3)
- Attack Surface Management (3)
- Awareness Week (3)
- EU AI Act (3)
- Hacking (3)
- ISO (3)
- Passwords (3)
- Press Release (3)
- AWS (2)
- Attack Surface (2)
- Business Continuity Planning (2)
- Cyber Security Law (2)
- ISO 27701 (2)
- Internal Audit (2)
- NIST 800 Series (2)
- Report (2)
- SDLC (2)
- Vendor Management (2)
- Vulnerability Management (2)
- Amazon (1)
- Assessment (1)
- Attestation (1)
- Audit (1)
- BCMS (1)
- Backup And Recovery (1)
- Blackbasta (1)
- CI (1)
- CMMC (1)
- COVID (1)
- Caas (1)
- Certification (1)
- Cloud (1)
- Competitive (1)
- Engineers (1)
- Ethical Hacking (1)
- Exercises (1)
- Grit (1)
- Hashcat (1)
- ISO 22301 (1)
- ISO 27018 (1)
- ISO 42005 (1)
- IaaS (1)
- Kahoot (1)
- Management (1)
- NIST 800-171 (1)
- OSINT (1)
- Outsourced Pci (1)
- P2pe (1)
- PIA (1)
- Pentest Report (1)
- Phishing (1)
- Privacy Impact Assessment (1)
- Privacy Shield (1)
- Ransomeware (1)
- Security Advisory (1)
- Soc2 (1)
- Strategy (1)
- System Backdoor (1)
- Tabletop (1)
- Vulnerability Scan (1)
- Wannacry (1)