Cybersecurity
Showing posts tagged with "Cybersecurity".
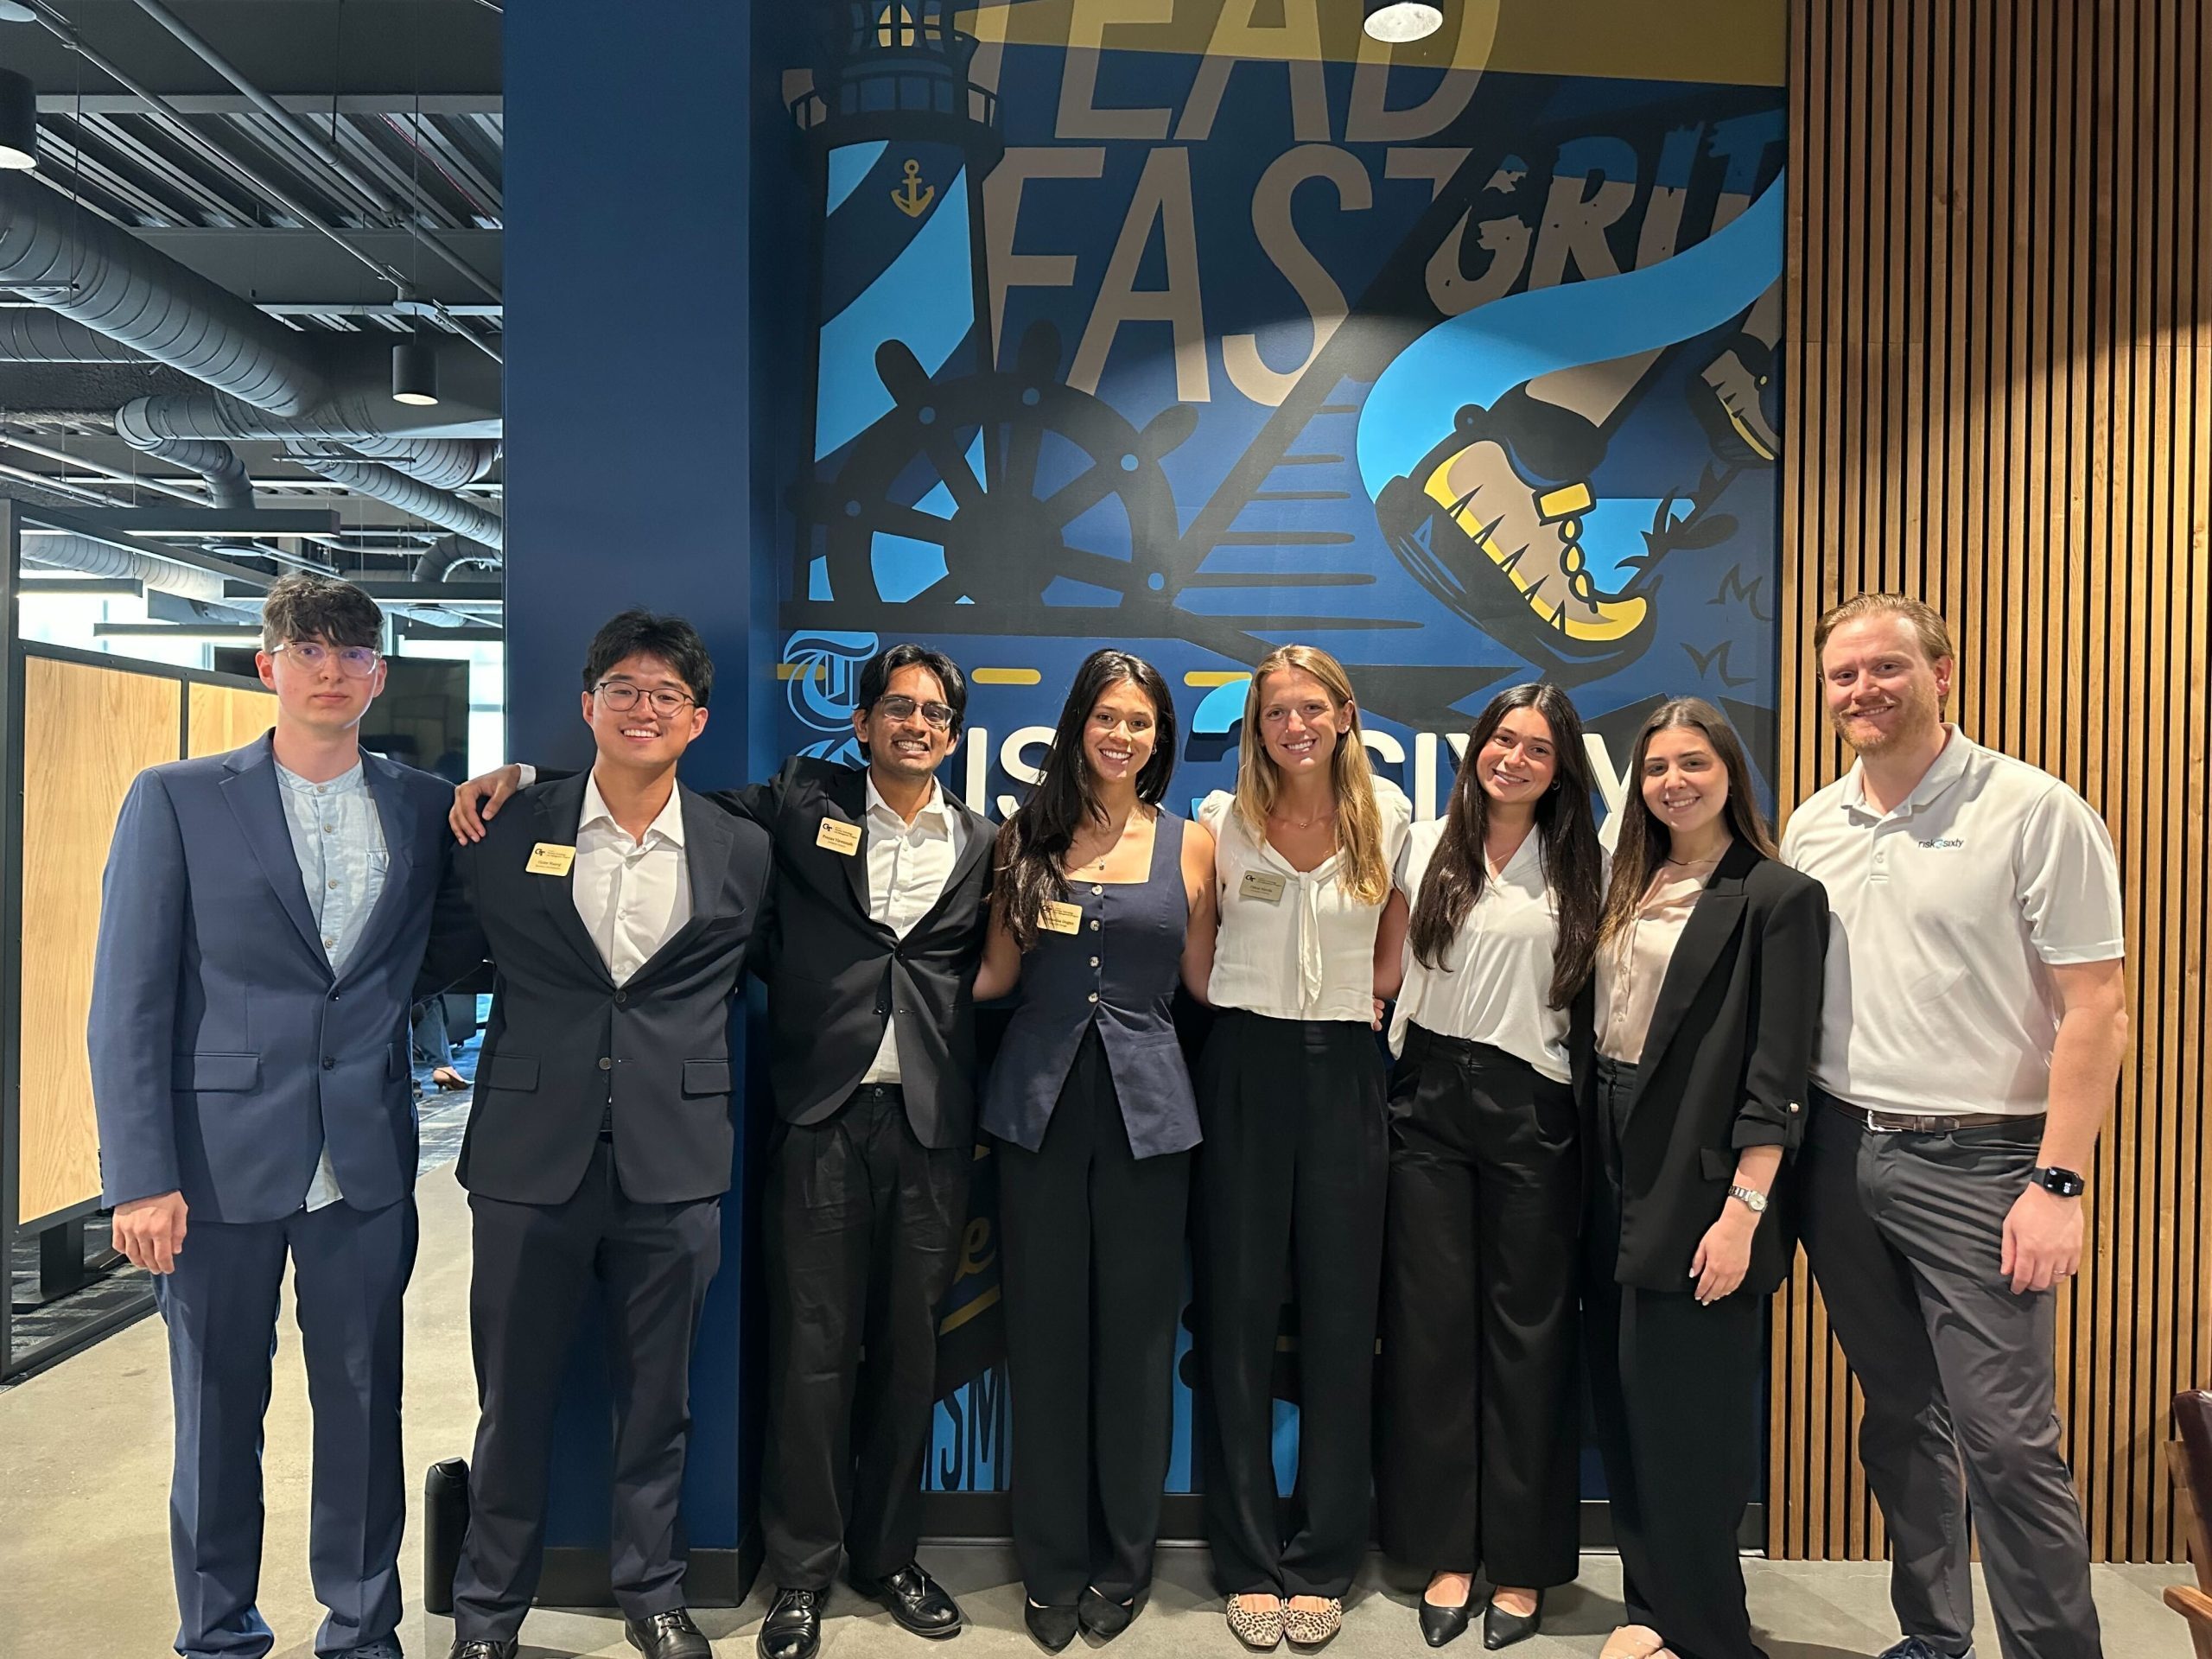
I am blown away by what Georgia Tech students are building right now.
risk3sixty was founded 10 years ago because Christian Hyatt and Christian White wanted to build a business aligned to their personal values. That mean…
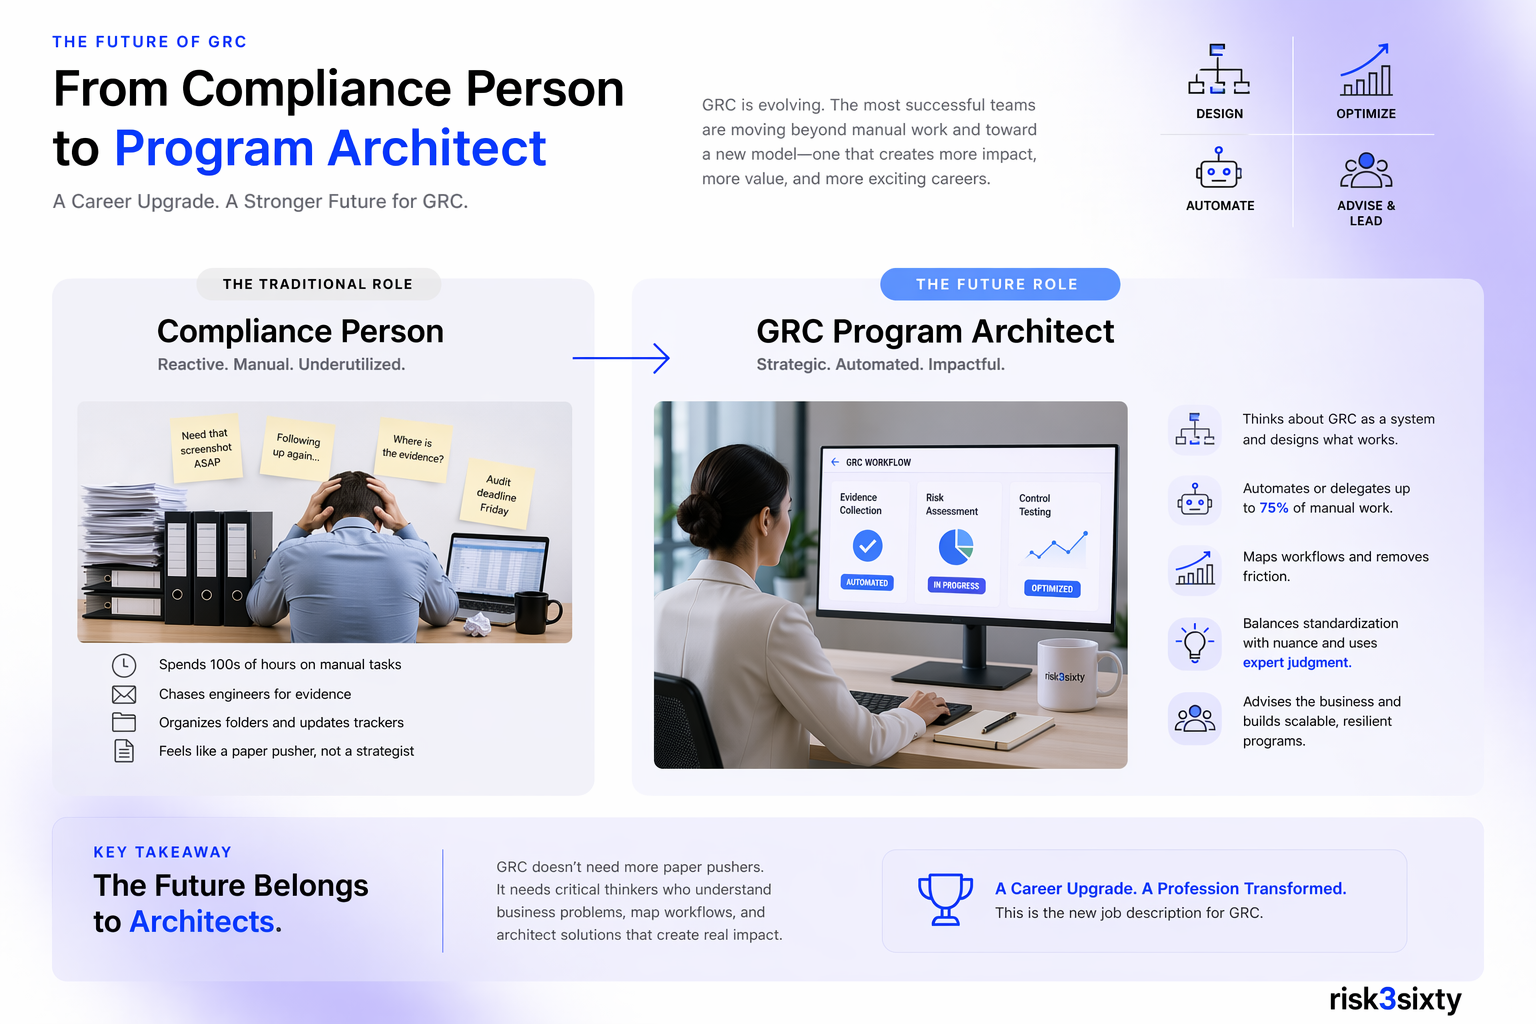
For years, too many talented people entered GRC expecting to do meaningful, high-impact work only to find themselves stuck chasing screenshots, organi…
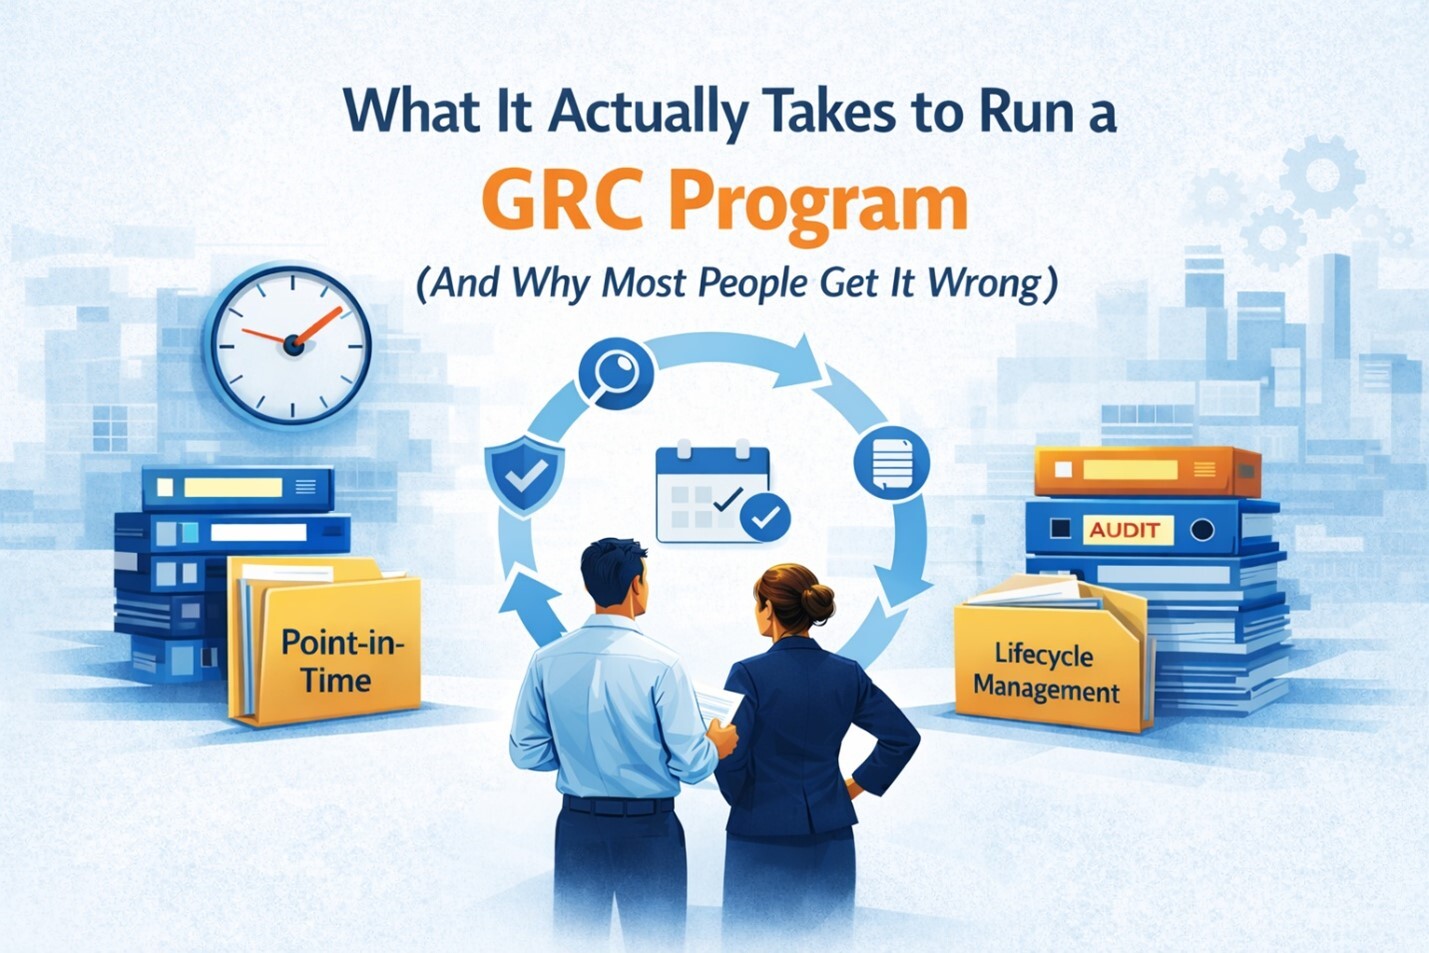
Most people think running a GRC program is about getting ready for audits.
As penetration testers and red team operators, we often find ourselves conducting engagements from Linux-based operating systems. This preference is p…
The rapidly evolving, complex cybersecurity landscape places Active Directory (AD) at the forefront of many cyber threats. As a crucial component of n…
Ensuring information security is necessary and a cornerstone of trust and reliability. Companies certified to ISO 27001 understand this but may need h…
We have unveiled a groundbreaking Compliance as a Service (CaaS) solution designed to streamline compliance processes for medium to large organization…
Trying to make sense of the Supreme Court’s recent Van Buren ruling? Below, is an easy-to-digest breakdown of the Court’s decision Brief Overview of V…
After you perform a risk assessment, what do you do with the results? Find out the answers to that and other common risk assessment questions in part …
Check out our webinar from Shane Peden and Christian Hyatt in which they discuss how to design a security program budget and get it approved. https://…
This blog post on developing and retaining security professionals at your high growth technology company is part of a multi-part series on designing a…
Tags
- Cyber Risk Management (59)
- IT Audit And Compliance (33)
- Penetration Testing (31)
- Cybersecurity (26)
- CISO Discussions (24)
- SOC Reporting (23)
- Security (22)
- Christian Hyatt (20)
- News And Events (20)
- ISO 27001 Compliance (19)
- Risk Management (19)
- ISO 27001 (18)
- SOC 2 (18)
- Compliance (17)
- Business (16)
- HITRUST (16)
- PCI DSS (13)
- Regulatory Compliance (12)
- Information Security (11)
- IT Audit (9)
- Webinars (9)
- CISO (8)
- Privacy (8)
- Penetration Test (7)
- Privacy Compliance (7)
- VCISO (7)
- Business Continuity (6)
- Cyber Risk (6)
- GRC Tool (6)
- ISO 42001 (6)
- Leadership (6)
- Compliance As A Service (5)
- Disaster Recovery (5)
- News (5)
- Risk Assessment (5)
- Training (5)
- BCAW (4)
- Cybersecurity Controls (4)
- GDPR (4)
- Network Security (4)
- Access Control (3)
- Artificial Intelligence (3)
- Attack Surface Management (3)
- Awareness Week (3)
- EU AI Act (3)
- Hacking (3)
- ISO (3)
- Passwords (3)
- Press Release (3)
- AWS (2)
- Attack Surface (2)
- Business Continuity Planning (2)
- Cyber Security Law (2)
- ISO 27701 (2)
- Internal Audit (2)
- NIST 800 Series (2)
- Report (2)
- SDLC (2)
- Vendor Management (2)
- Vulnerability Management (2)
- Amazon (1)
- Assessment (1)
- Attestation (1)
- Audit (1)
- BCMS (1)
- Backup And Recovery (1)
- Blackbasta (1)
- CI (1)
- CMMC (1)
- COVID (1)
- Caas (1)
- Certification (1)
- Cloud (1)
- Competitive (1)
- Engineers (1)
- Ethical Hacking (1)
- Exercises (1)
- Grit (1)
- Hashcat (1)
- ISO 22301 (1)
- ISO 27018 (1)
- ISO 42005 (1)
- IaaS (1)
- Kahoot (1)
- Management (1)
- NIST 800-171 (1)
- OSINT (1)
- Outsourced Pci (1)
- P2pe (1)
- PIA (1)
- Pentest Report (1)
- Phishing (1)
- Privacy Impact Assessment (1)
- Privacy Shield (1)
- Ransomeware (1)
- Security Advisory (1)
- Soc2 (1)
- Strategy (1)
- System Backdoor (1)
- Tabletop (1)
- Vulnerability Scan (1)
- Wannacry (1)