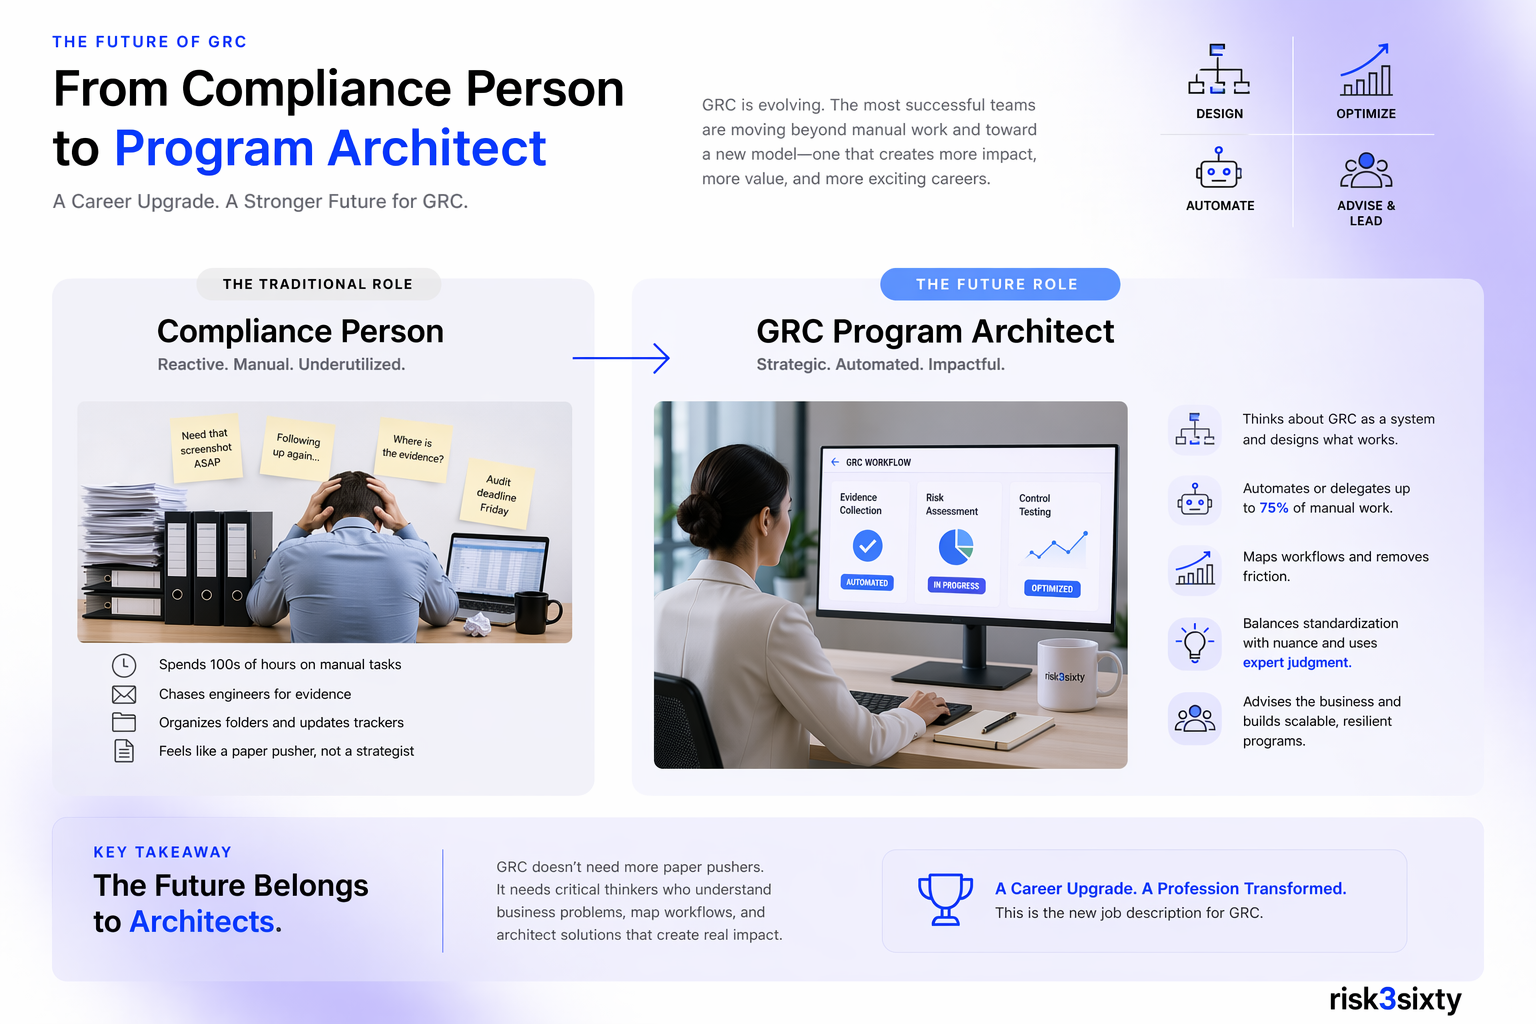
For years, too many talented people entered GRC expecting to do meaningful, high-impact work only to find themselves stuck chasing screenshots, organi…
We have unveiled a groundbreaking Compliance as a Service (CaaS) solution designed to streamline compliance processes for medium to large organization…
Many organizations are in search of ways to streamline their compliance efforts. See how the HITRUST CSF can enable a “Single Framework Strategy” that…
The AICPA-designated SOC 2 framework is used to express an opinion on controls over security, privacy, availability, confidentiality, and processing i…
A GRC tool can provide many benefits to your GRC program. However, before you chase shiny objects, you must understand what a GRC program is and how a…
So, you’ve been tasked with providing evidence for an audit. You may be wondering what your auditor is even looking for. Let’s take a look behind the …
A GRC tool can help an organization manage its governance, risk, and compliance program. But why use a GRC tool instead of managing your GRC program m…
How should a company think about PCI Scope and Segmentation? For companies looking to identify and reduce the scope of their PCI environment, through …
In this blog, we’ll dive into one of the most important parts of a SOC 2 report, the SOC 2 System Description! During your due diligence process, a ve…
Do your business continuity plans account for your company’s compliance and regulatory requirements? For many, the answer to that question is “no”. An…
Maintain Compliance From our experience working with high-growth technology companies subject to a myriad of compliance obligations, maintaining secur…
Key areas of overlap to help you harmonize workstreams. The compliance universe is ever-expanding. In addition to various information security require…