
New Perspective
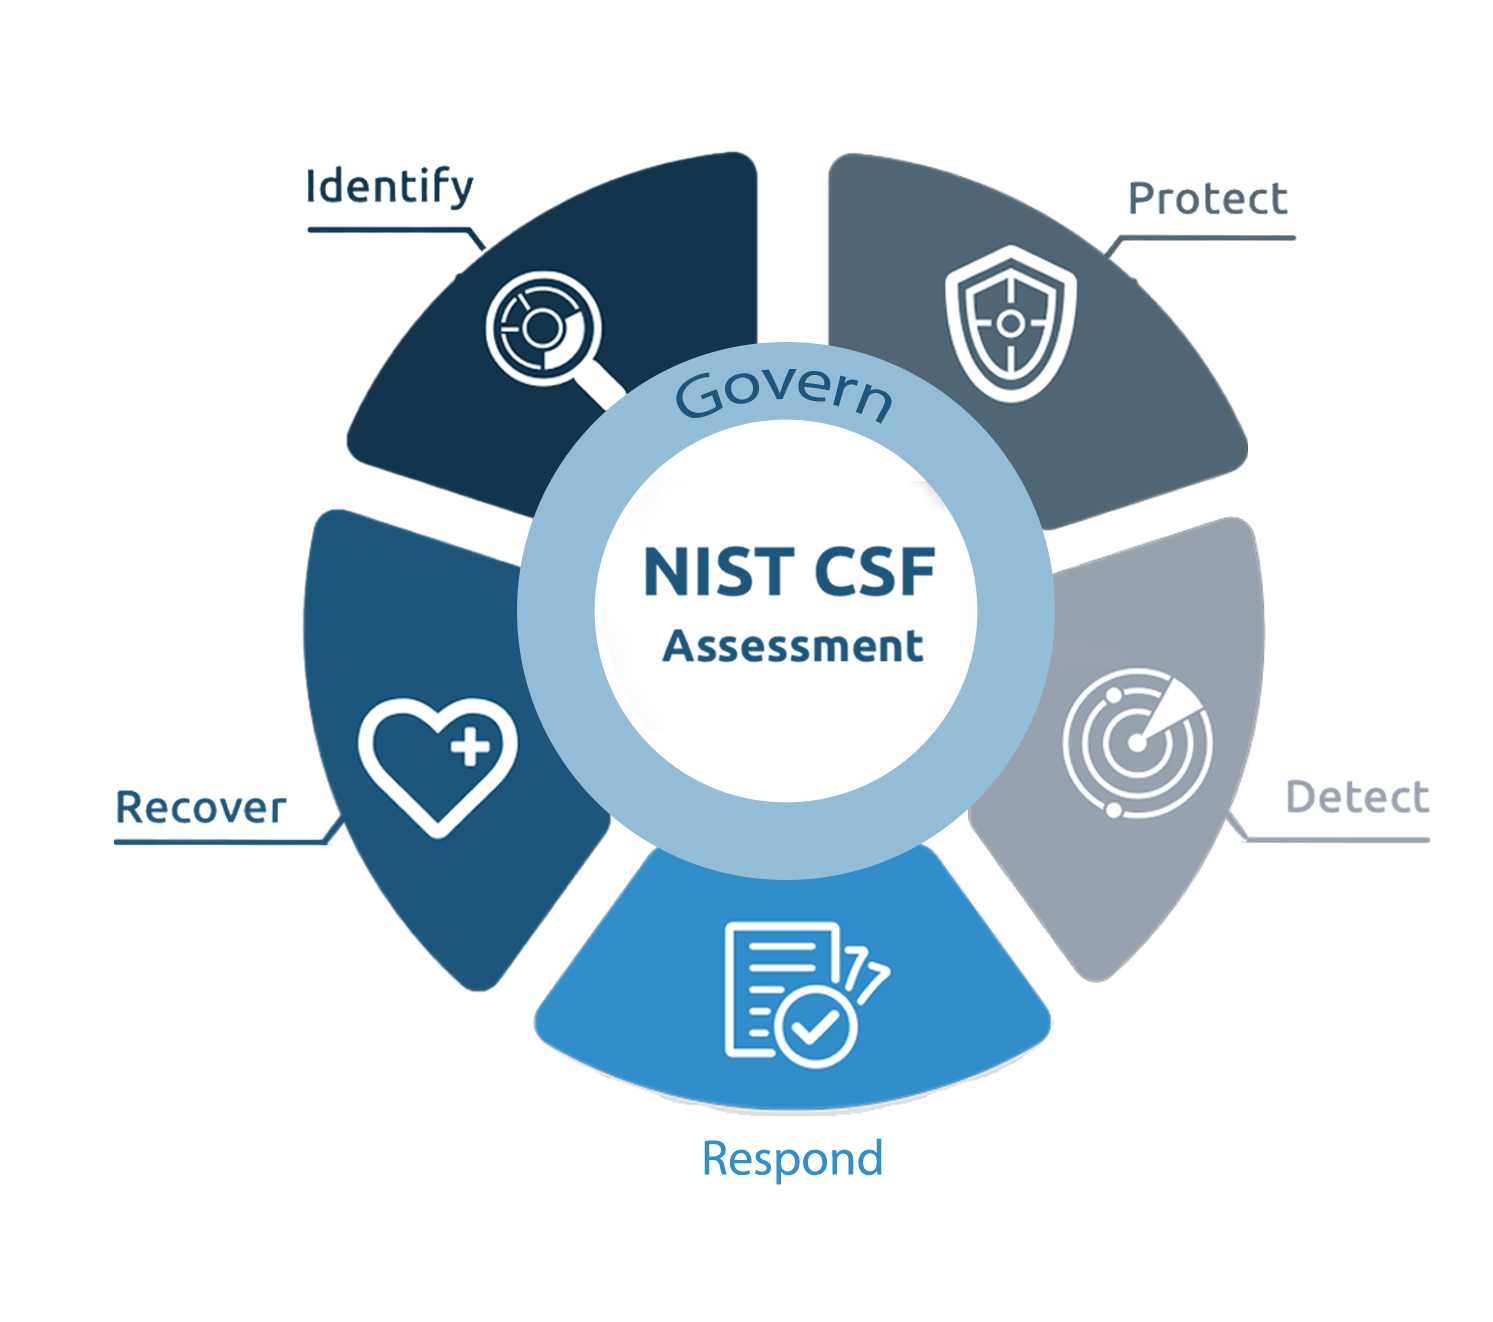
Your executive team seeks an independent evaluation of your cybersecurity program's current maturity to guide strategic decisions and resource allocation.
More Strategic Guidance
Gain actionable insights to identify strengths, areas for improvement, and opportunities to enhance your cybersecurity strategy.
Objective Evaluation
Receive a clear, unbiased assessment of your current cybersecurity maturity, tailored to your organization’s specific needs.
Executive Workshop
We begin by gaining insights from executives on the following:
- The business's operational structure
- Leadership's key priorities and concerns
- Core business objectives
- How security initiatives align with and support these objectives
- The alignment between Security, IT, and overall business goals
- Security program KPIs and success metrics
IT and Security Landscape Review
We then perform a technical deep dive with security and IT stakeholders to uncover the following:
- Network and IT Environment Layout
- Critical Security Controls (Lines of Defense)
- Product Architecture
- High Level Flow of Sensitive Data
Critical Artifact Review
Based on insights gathered during the executive workshop and technical deep dive, our team requests relevant artifacts for review. These typically include:
- Recent internal and external scan reports
- Current security KPI dashboard
- Recent penetration testing results and methodology
- The latest cyber risk assessment
- Information security policies and standards
- Stakeholder workshops
Analysis and Reporting
We analyze all evidence, artifacts, and meeting notes, assigning scores across people, processes, policies, and technology. We then produce a comprehensive report that includes:
- Identified strengths
- Rationales behind the assigned scores
- Notable findings
- Key recommendations for enhancing maturity
See how Platform.sh saved 75% by harmonizing SOC 2, PCI DSS, and HIPAA.

Joey Stanford
VP of Security & Privacy
Salesloft obtained certification across SOC 2 and ISO 27001 in one harmonized workstream.

Mike Meyer
SVP of Security
Fullstory harmonized 10 frameworks and becomes ISO 42001 early adopter

Anne Turner
Director of GRC
Expert Team
Full team of certified industry experts.
fullCircle GRC Platform
Centralized command center to unify multiple frameworks.
Award-Winning
Consulting Magazine Best Firms to Work For.
Proven Success
Experience from over 1,000 engagements.