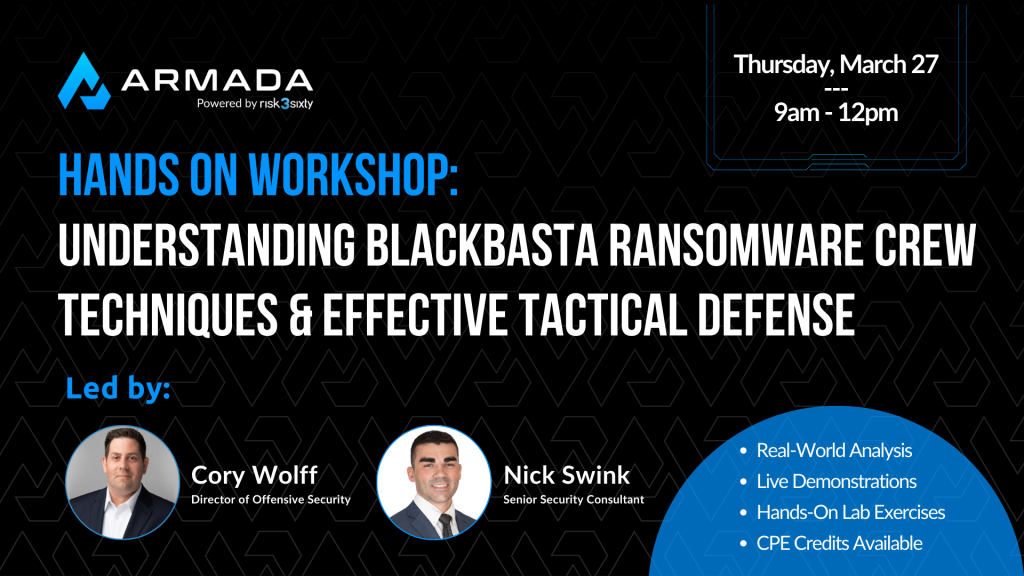
Hands-On Workshop
Blackbasta Ransomware Crew Techniques & Effective Tactical Defense
Thursday, March 27th | 9am-12pm
This workshop covers the sophisticated tactics, techniques, and procedures (TTPs) employed by the Blackbasta ransomware group, drawing directly from recently leaked chat logs that provide insight into day-to-day ransomware operations.
These real communications reveal the group’s actual planning, execution strategies, and internal discussions—offering a rare window into how modern ransomware crews truly operate.
What You'll Learn:
- Identify key TTPs used by the Blackbasta ransomware group
- Understand the methodology behind modern ransomware campaigns
- Recognize early warning signs of a potential Blackbasta infiltration
- Implement specific defensive controls to mitigate Blackbasta attack vectors
What You'll Get:
- Real-world conversations with technical evidence on how attacks were executed
- Strategies to implement for effective defensive countermeasures
- Combination of presentation, live demonstrations, and hands-on lab exercises
- Practical skills to detect, prevent, and respond to ransomware threats
Register Now & Reserve Your Spot for the FREE Live Workshop
Workshop Details
CPE Credits: For this specific workshop, participants will earn 3.0 credits.
*CPE credits will be issued 24 hours via email to each participant.
Field of Study: Information Technology: Encompasses subjects related to information technology, AI, Blockchain, Cloud Computing, Computer Systems, Cyber security, Management Information Systems, etc.
Required Elements of Engagement: Polling
Additional Information: Prerequisites: Basic knowledge of Microsoft Windows, Azure, and EntraID. Advanced Prerequisites: None Program Level: Basic
This workshop is designed for:
- Corporate audience with a basic understanding of cybersecurity concepts.
- Offensive security professionals looking to emulate specific adversaries.
- Security professionals looking to improve their defenses against ransomware crews.
- Real-world examples and case studies will be used to illustrate key points.
risk3sixty is registered with the National Association of State Boards of Accountancy (NASBA) as a sponsor of continuing professional education on the National Registry of CPE Sponsors. State boards of accountancy have final authority on the acceptance of individual courses for CPE credit. Complaints regarding registered sponsors may be submitted to the National Registry of CPE Sponsors through its web site: www.nasbaregistry.org. For more information regarding administrative policies such as complaint, please contact risk3sixty L&D program facilitator Jessica Andree at jessica.andree@risk3sixty.com or sponsor Philip Brudney at philip.brudney@risk3sixty.com.
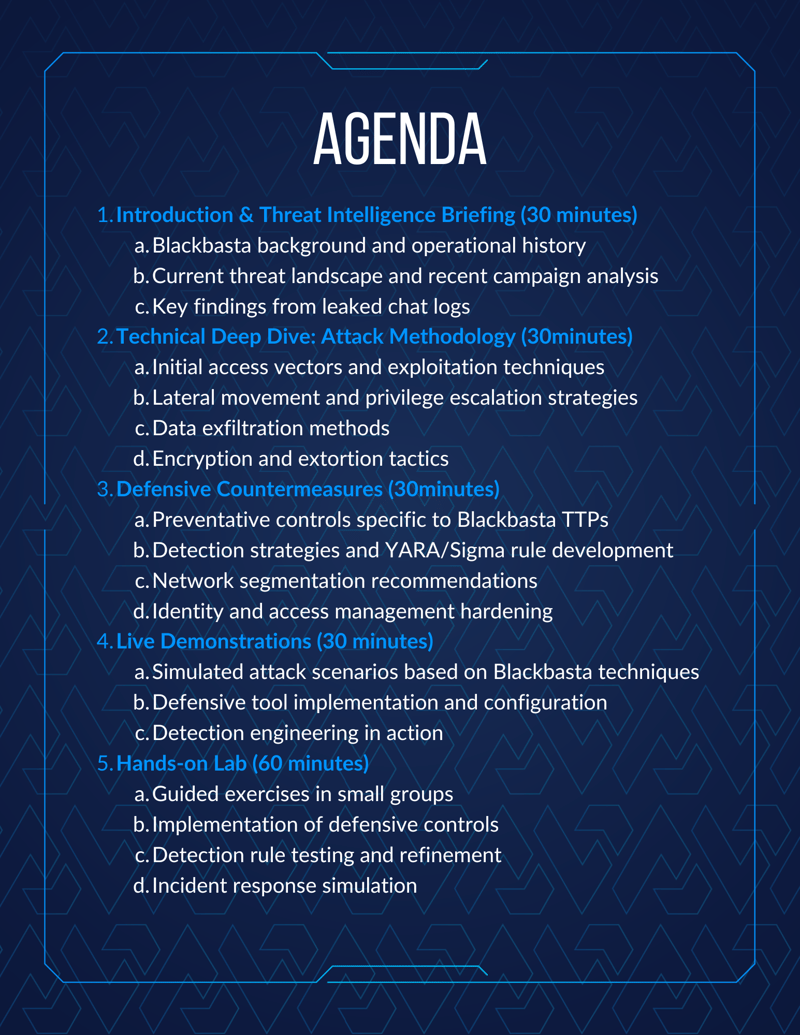
The workshop content is subject to change based on the latest developments and available information.
Meet the Presenters
Cory Wolff
Director of Proactive Services
With over 20 years of experience in IT, security, and development, Cory Wolff is a passionate and skilled hacker who leads the offensive security practice at risk3sixty, a consulting firm that helps clients navigate complex cybersecurity and compliance challenges. He holds multiple certifications, including the Offensive Security Certified Professional (OSCP) and the Certified Information Systems Security Professional (CISSP), and has a proven track record of building and breaking various technologies since his first computer in 1988.
As the Director of Proactive Services, Cory oversees the delivery of high-quality penetration testing, red teaming, and vulnerability assessment services to a diverse range of clients across different industries and sectors. He also contributes to the cybersecurity community as a core team member of Red Team Village, a platform that fosters collaboration, learning, and innovation among red teamers and security professionals. Cory’s mission is to help organizations improve their security posture, protect their assets, and achieve their goals.
Nick Swink
Senior Security Consultant
Nick Swink is a Sr. Security Consultant at risk3sixty specializing in penetration testing, red teaming, and adversary simulation. With a passion for malware development and red team tooling, he has created multiple popular open-source tools that contribute to the offensive security community. Nick has spoken at DEFCon’s Red Team Village and hosts informational webcasts on advanced offensive security techniques.
Holding certifications such as PNPT, OSCP, and CRTL, he brings deep expertise in adversary emulation, helping organizations identify and remediate security weaknesses. Through real-world threat simulation, Nick works to enhance security programs, improve detection capabilities, and stay ahead of evolving attack techniques.
Raving Fans