LIVE WEBINAR | Thursday 11/19 @ 1pm EST
AIUC-1: Implementation to Certification
Part 4 in the AIUC-1 Webinar Series
The gap between “we built the controls” and “we can prove it” is where certification timelines usually slip.
Join experts from risk3sixty and Schellman for a practical walkthrough of the full AIUC-1 journey, from the first scoping decision to a signed certificate. We'll cover what implementation looks like control by control, the technical evidence auditors expect to see, and where organizations lose time between building a control and being able to demonstrate it.
As the capstone of the series, this session puts the implementor and the auditor in the same room so teams get an honest picture of both sides of certification before they’re in the middle of one.
What You’ll Learn:
- How to scope the AIUC-1 control set, close gaps, and build out controls before an audit begins
- What technical evidence auditors expect for controls like logging, guardrails, and adversarial testing
- How audits are scoped, sampled, and tested, and what separates a smooth audit from a painful one
- How to sequence implementation, evidence collection, and readiness, plus a practical checklist you can put to work right away
Register Now to save your seat and access to previous sessions
Meet the Presenters
Grace Pfohl
Senior Consultant & AI Advisory Team Lead, risk3sixty
Grace Pfohl is a Senior Consultant on risk3sixty’s ethOS Compliance Consulting team and serves as the AI Advisory Team Lead. She leads AI governance, security, and privacy engagements, helping organizations implement ISO/IEC 42001 programs as part of broader compliance initiatives through audits, risk assessments, and AI management system implementations.
With a strong technical background and deep specialization in AI governance, Grace has played a key role in helping organizations achieve some of the earliest ISO/IEC 42001 certifications. She works closely with clients to implement AI management systems aligned with emerging global standards, translating regulatory requirements into practical, risk‑based governance programs.
Grace holds both BS and MS degrees in Computer Science from the Georgia Institute of Technology, with a specialization in Human‑Computer Interaction. She is a certified ISO 42001 Lead Auditor and Implementer and regularly guides organizations through ISO 42001 implementations and internal audits, helping operationalize responsible AI practices at scale. She is also an active member of the WiCyS community, sharing applied perspectives on AI governance and responsible AI.
Christian Hyatt
CEO & Co-Founder, risk3sixty
Christian is the CEO and Co-founder of risk3sixty. He is responsible for setting the vision for the team, ensuring the leadership team is “rowing in the same direction,” creating purpose and alignment across the firm, and nurturing company culture.
With experience overseeing over 2000 cybersecurity engagements, Christian is one of the most experienced experts in the nation. Christian is a best selling author of the critically acclaimed cybersecurity leadership book “Security Team Operating System“. Under Christian’s leadership, risk3sixty has been named 3-time Consulting Magazine’s Best Firms to Work For, 7-time Atlanta’s Fastest Growing companies, 7-time Atlanta’s Best Places to Work, 3-time HireVets Platinum Honoree, and was named Top 100 CEOs in Atlanta.
Christian has an M.B.A. from Georgia Tech and a B.B.A. from the University of Georgia. Christian is a Georgia Tech Technology and Management (T&M) corporate partner and Advisory Board Member for UGA’s Management Information System Advisory Board.
Danny Manimbo
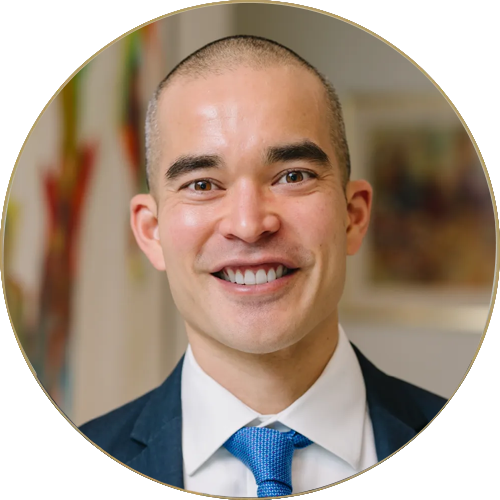
Managing Principal, Schellman
Danny Manimbo is a Principal at Schellman based in Denver, Colorado, where he leads the firm’s Artificial Intelligence (AI) and ISO services and serves as one of Schellman’s CPA principals. In this role, he oversees the strategy, delivery, and quality of Schellman’s AI, ISO, and broader attestation services. Since joining the firm in 2013, Danny has built more than 15 years of expertise in information security, data privacy, AI governance, and compliance, helping organizations navigate evolving regulatory landscapes and emerging technologies. He is also a recognized thought leader and frequent speaker at industry conferences, where he shares insights on AI governance, security best practices, and the future of compliance. Danny has achieved the following certifications relevant to the fields of accounting, auditing, and information systems security and privacy: Certified Public Accountant (CPA), Certified Information Systems Security Professional (CISSP), Certified Information Systems Auditor (CISA), Certified Internal Auditor (CIA), Certificate of Cloud Security Knowledge (CCSK), and Certified Information Privacy Professional – United States (CIPP/US).